
02 · from the workshop
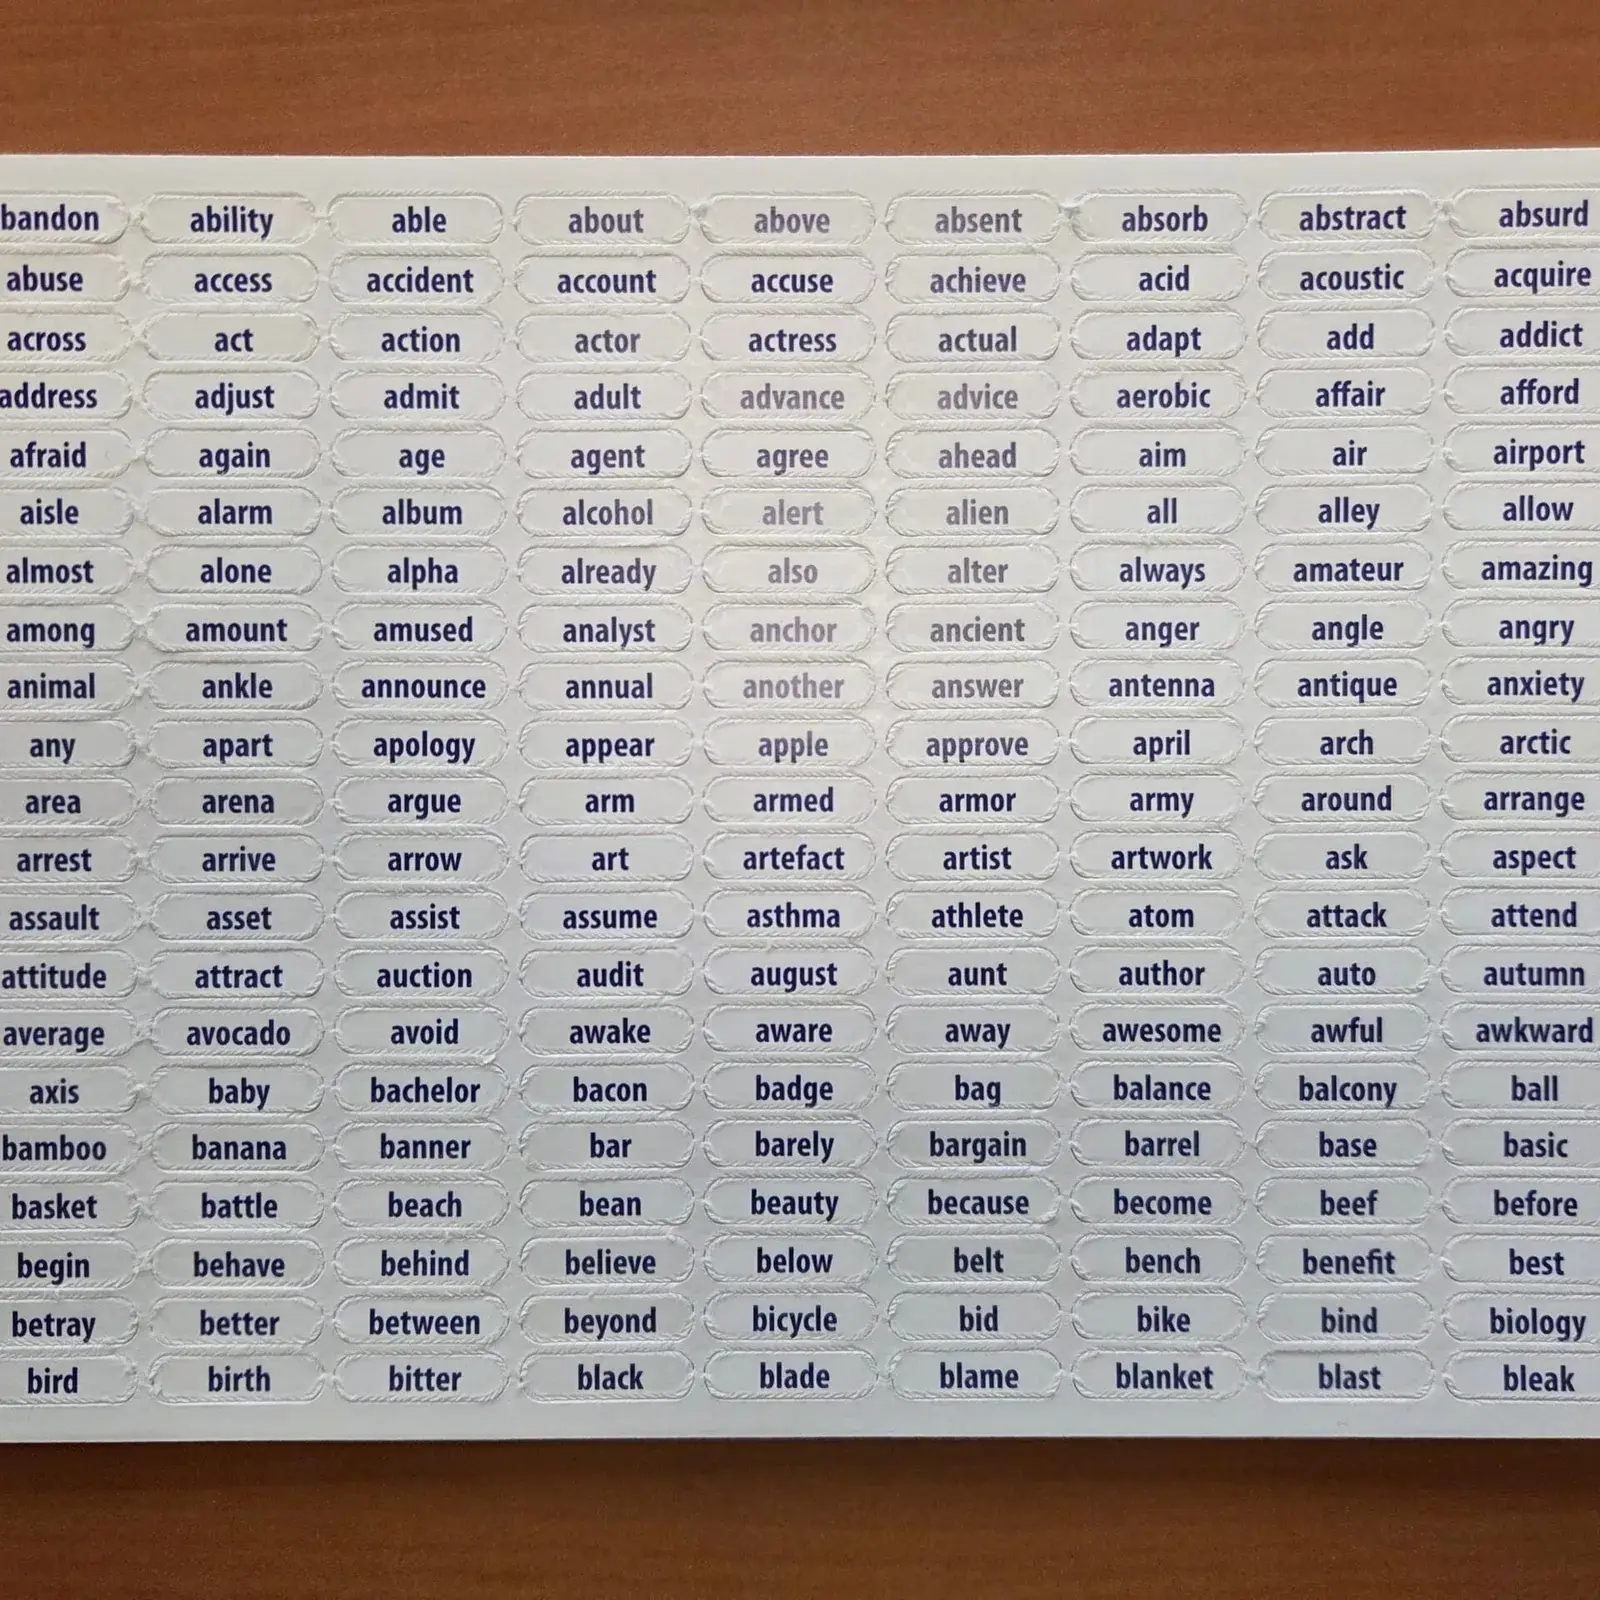
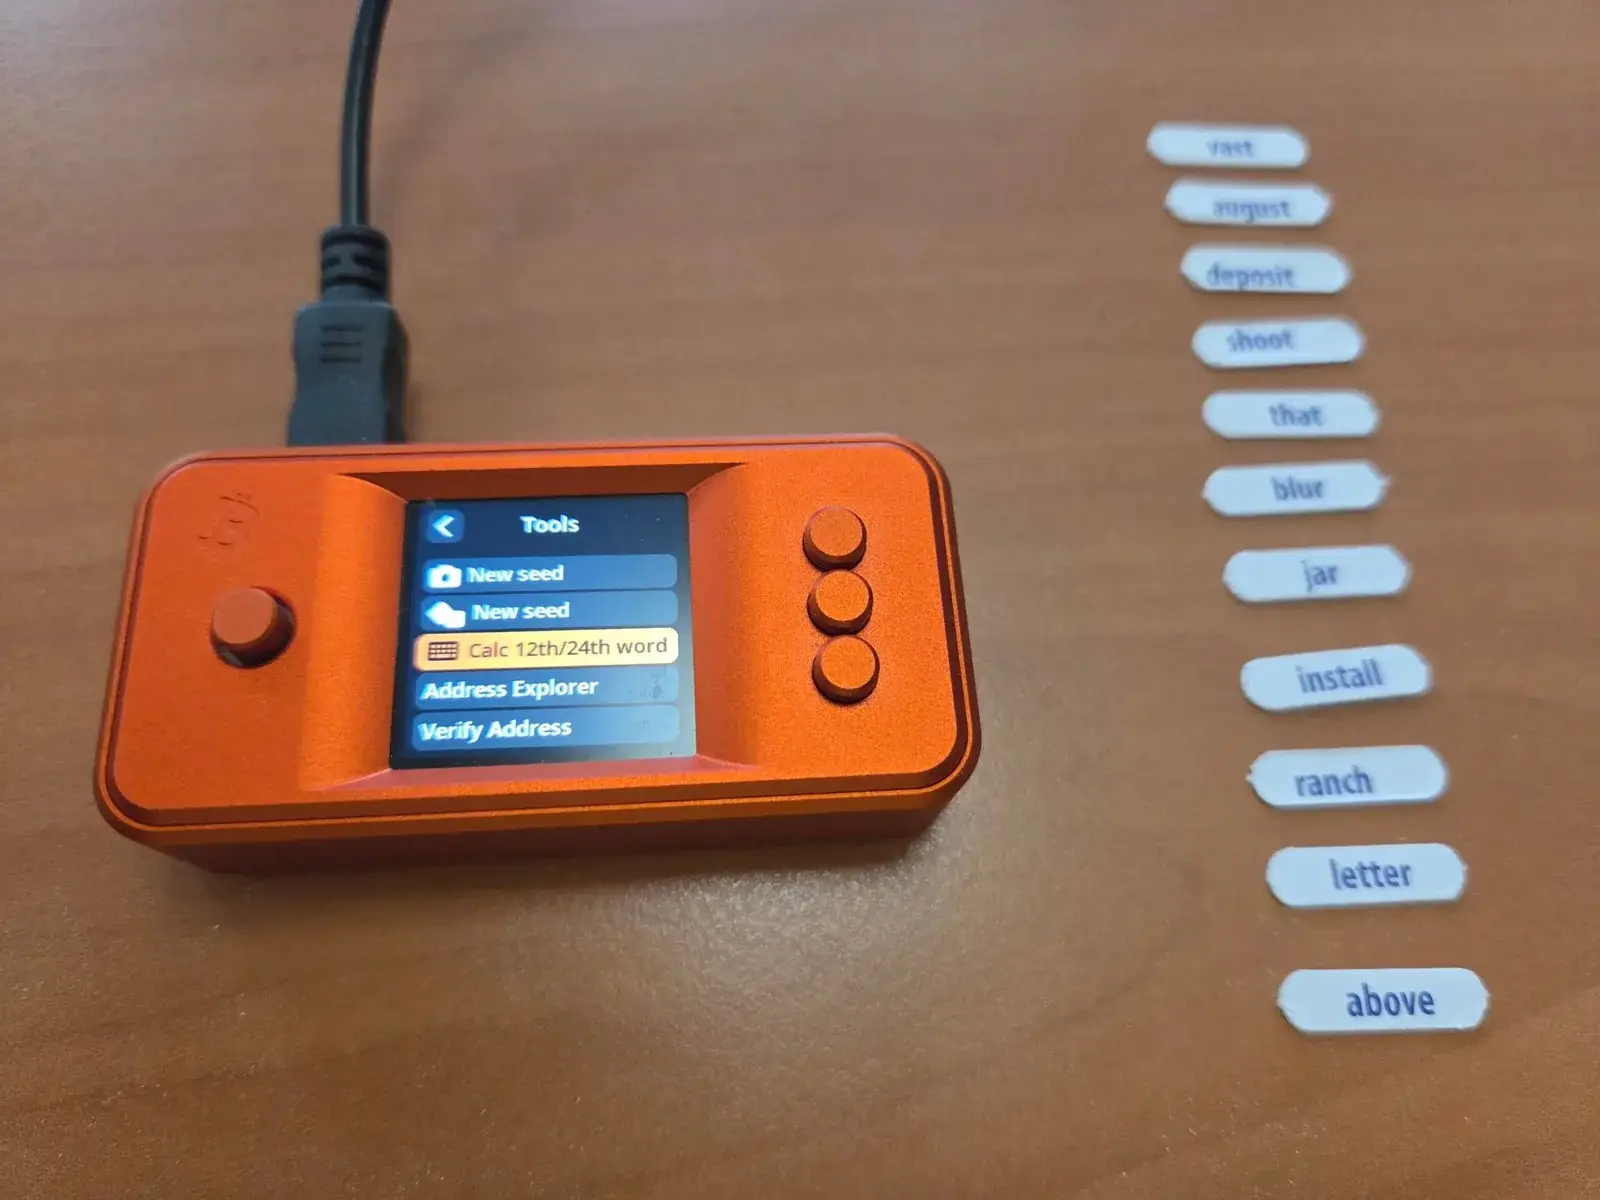
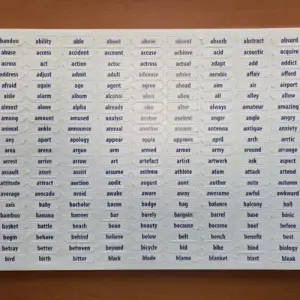
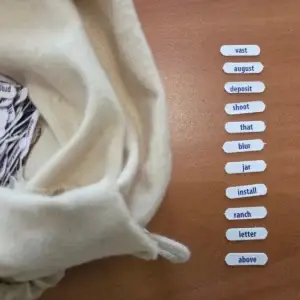
How can you be sure that your hardware wallet’s seed phrase is truly random? Usually, you can’t be sure: you have to trust the random number generator and the device’s firmware. With Shuffle Seed, you generate that randomness yourself. All 2,048 words from the BIP39 word list are printed on six sheets as expression cards. You shuffle them in a bag, blindly draw your words, and let your wallet calculate only the last word.
How does Shuffle Seed work?
In short: you create the randomness with your hands and your wallet only does the final calculation. In six steps from skin to seed:
- Check. Compare the six alphabetical sheets with the official BIP39 wordlist on GitHub. Trust, but verify.
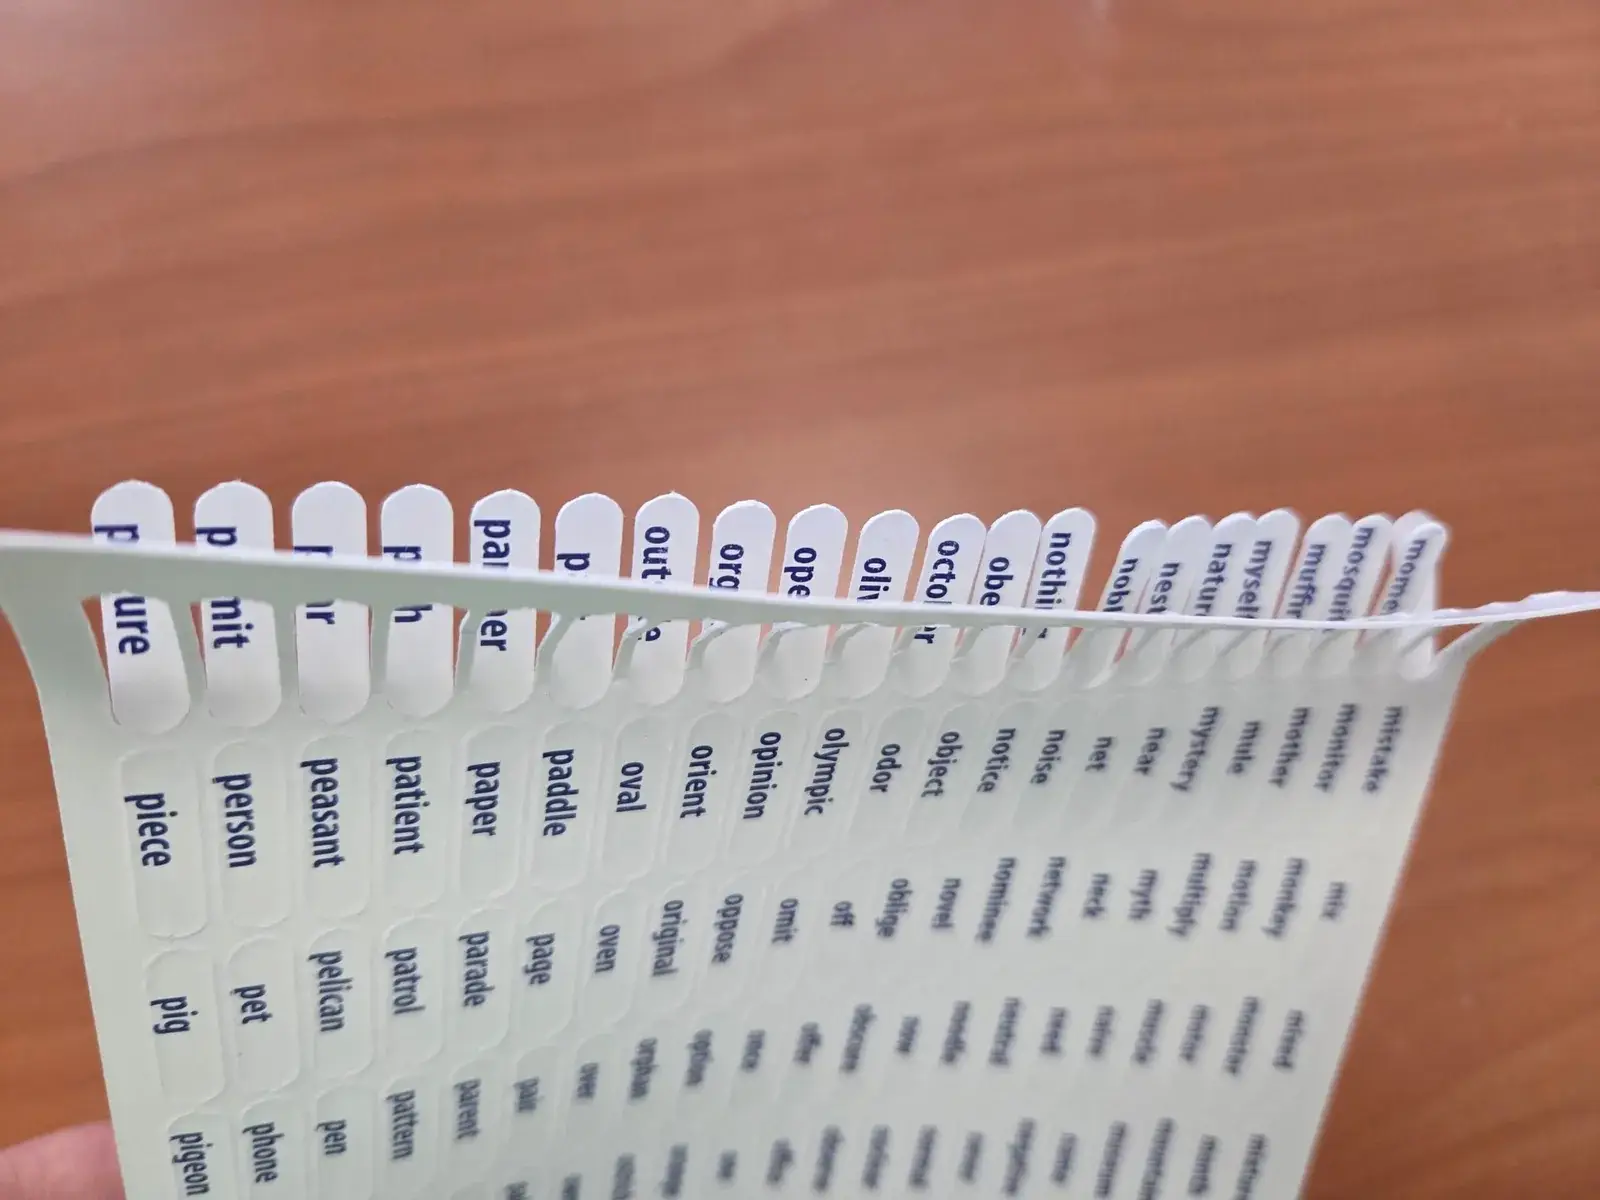
- Express the words. All 2048 tokens come loose from the sheets.
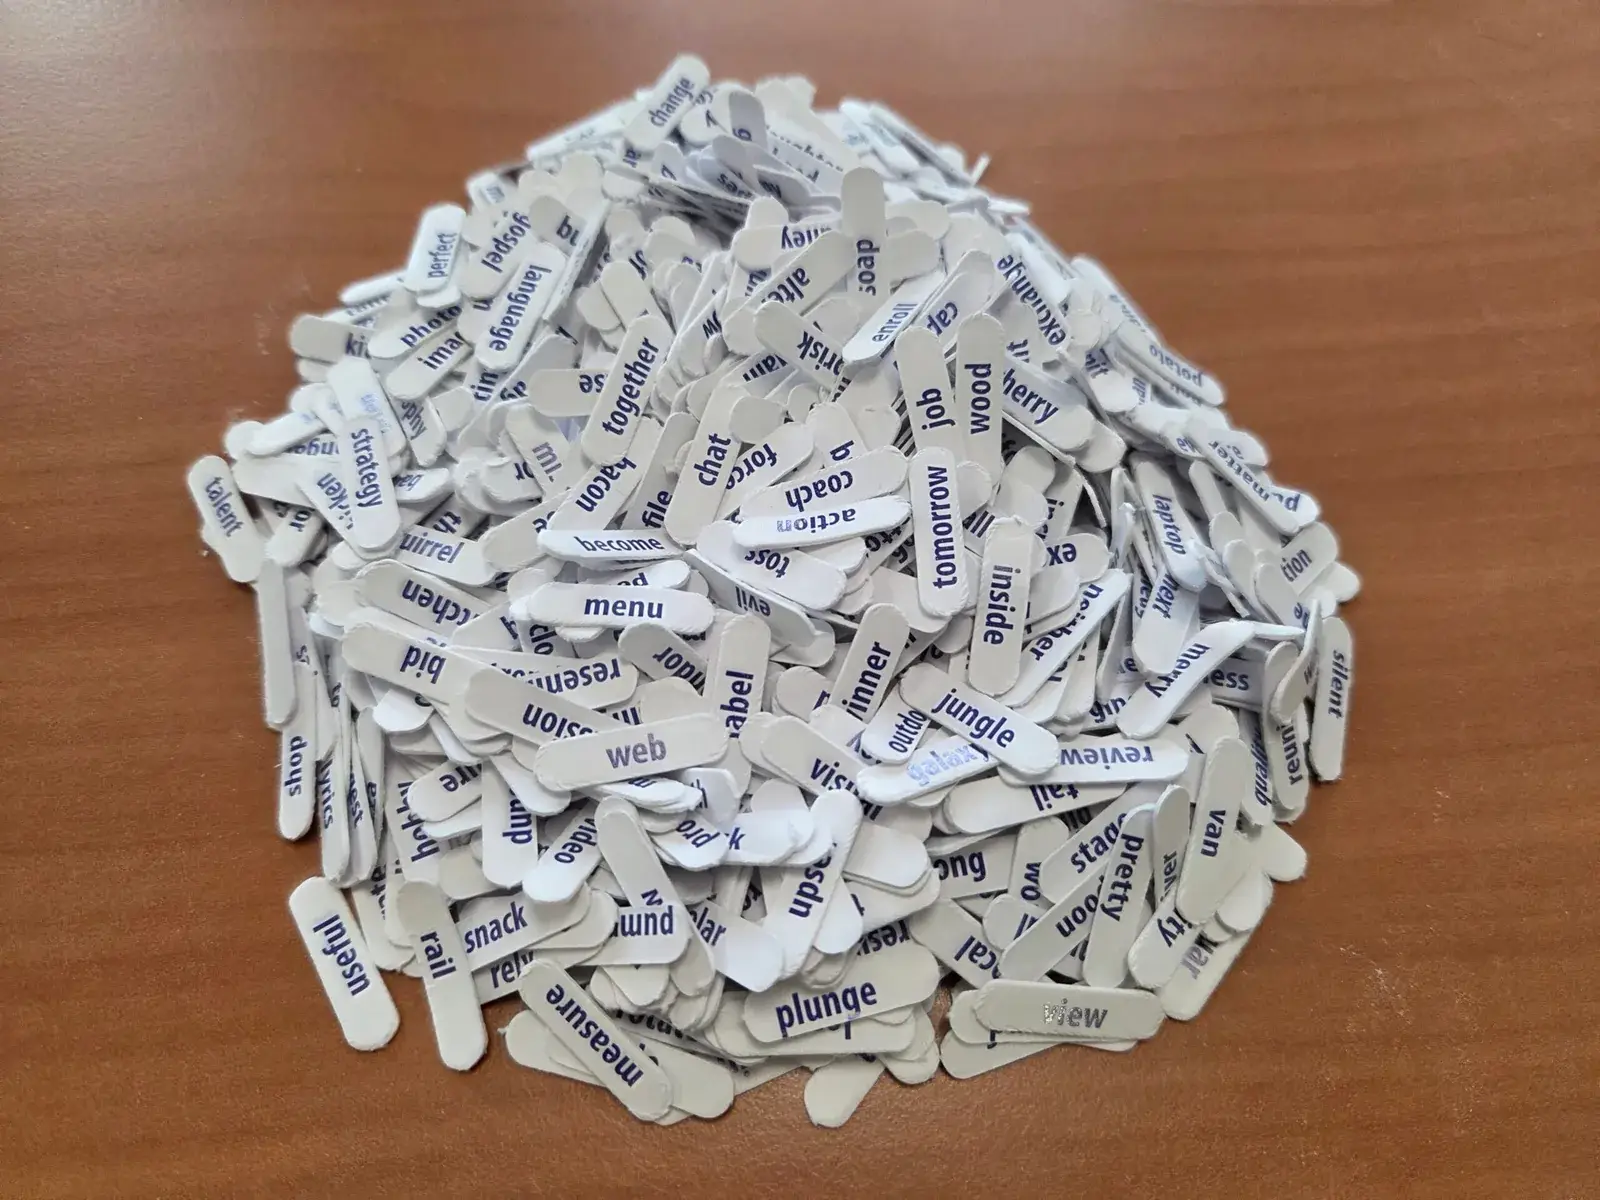
- Shake. Put all the chips in a bag or hat and mix them thoroughly.
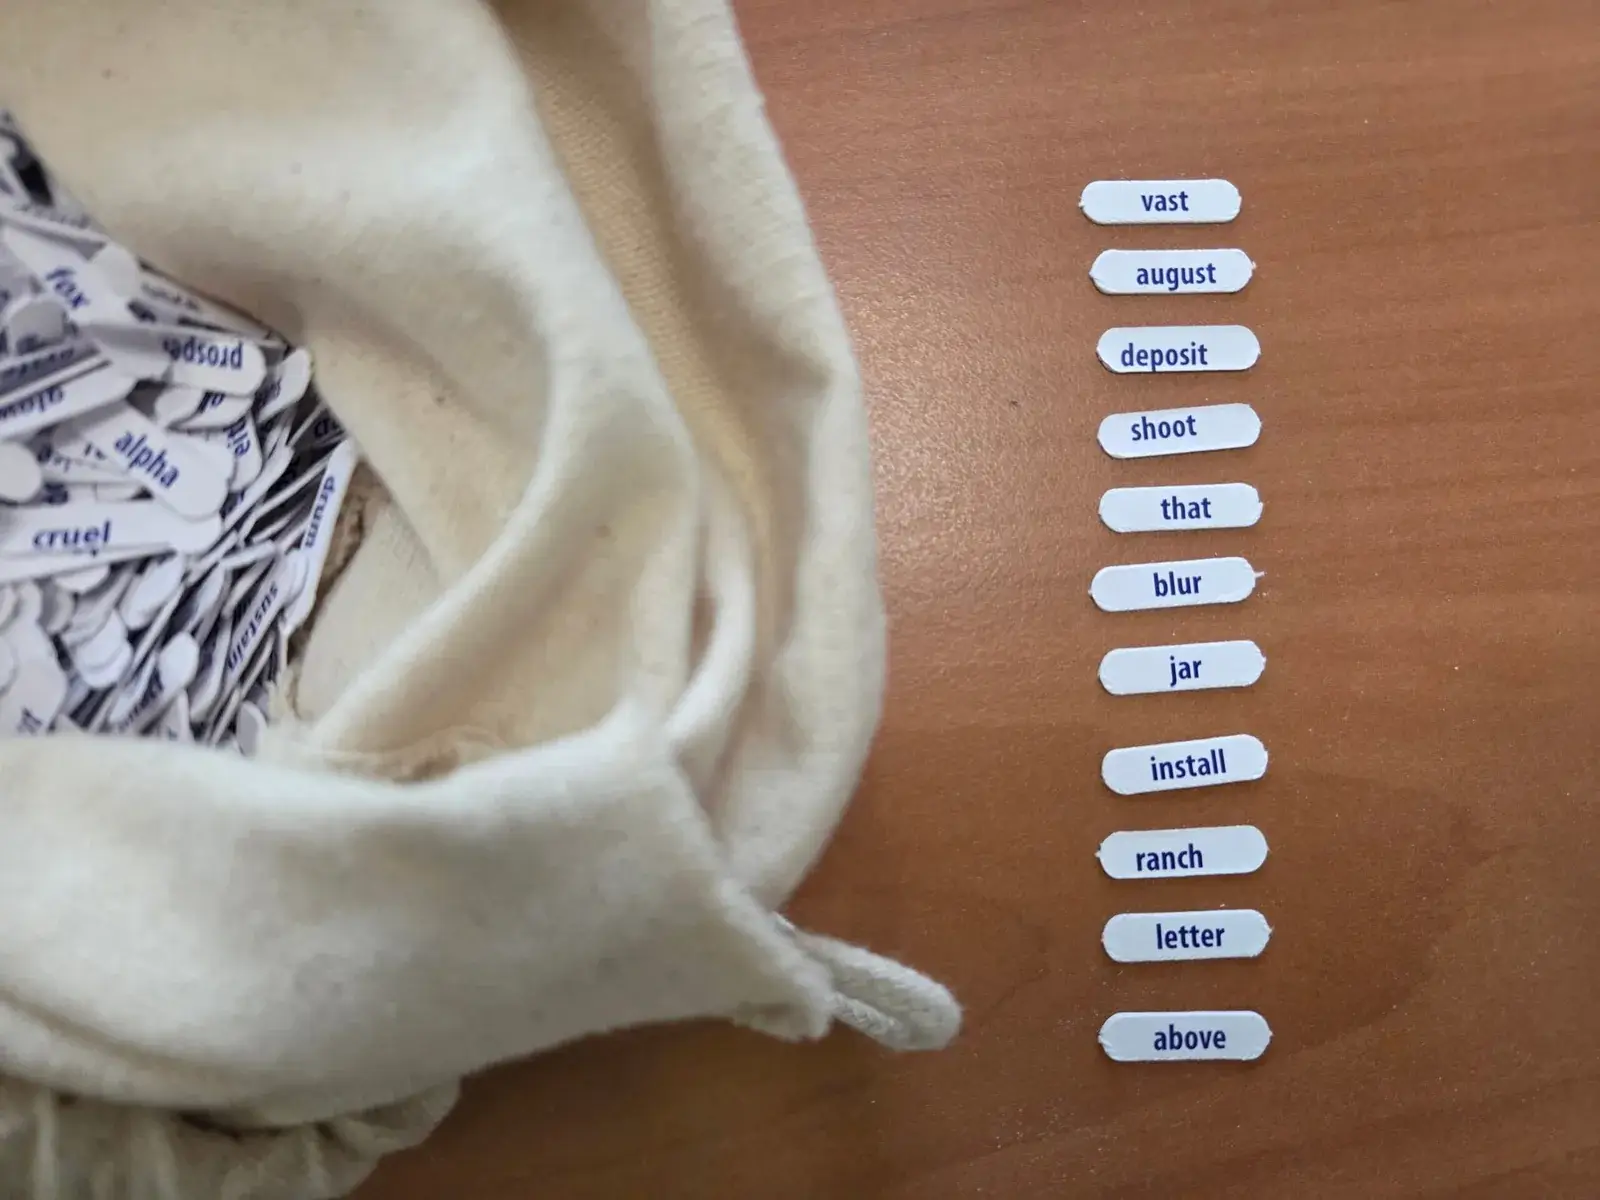
- Blind hike. Eleven words for a 12-word seed, 23 for a 24-word seed. One by one, and put each token back before you draw the next. Duplicate words are allowed.
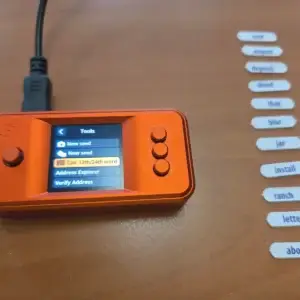
- Have the last word calculated. The twelfth or twenty-fourth word contains the checksum and cannot be extracted. Your hardware wallet or signing device calculates it for you.
- Make a backup in steel. Never store your seed digitally. For example, engrave it into a Seedfan Steel Kit and keep it in a safe place.
Why would you save your own seeds?
A hardware wallet generates your seed using a built-in random number generator. With a good device, that’s fine, but you can’t verify it. If there’s a flaw in the firmware or the chip, you won’t notice it until it’s too late. You can read about why this isn’t just a theory in our article on the Coldcard entropy problem.
With Shuffle Seed, you’re in full control of the randomness. Each blind draw with replacement yields 11 bits of entropy, since you’re choosing from 2,048 possibilities. Twenty-three draws yield roughly 253 bits. That’s on the same order of magnitude as the 256 bits that a hardware wallet uses itself and is well beyond the reach of any brute-force attack. The wallet simply fills in the checksum word and verifies that the seed is valid.
Shuffle Seed or dice?
Rolling dice is the well-known way to create entropy yourself. It works, but it requires 100 rolls, flawless note-taking, and a wallet that converts the sequence into 24 words. That conversion happens out of sight. If you want to verify it, you have to rebuild the device's calculation yourself.
Shuffle Seed skips that step. What you draw are already BIP39 words. You see your seed being created, you can compare it with what your wallet shows, and you can check it on a second offline device. Fewer actions, less chance of error, and a process that a beginner understands and an advanced user can verify.
Who is Shuffle Seed for?
For anyone who takes self-custody seriously and prefers not to have the word “trust” in their setup. New to self-custody? Read first Keep the bitcoin Starter Guide for yourself. Then choose a hardware wallet that can calculate the checksum. It also works as a gift for a bitcoiner: it's tangible, educational, and you don't need to know anything about it yourself to give it.
Note: generate your seed in a secure room, without cameras, windows, or onlookers. Do not photograph your words and never type them into a device with internet access. How you store the seed afterwards can be read in store seed phrase securely: paper or steel.

Reviews
There are no reviews yet.